sub rosa by naiveHA
| Repo: | IzzyOnDroid |
| AppID: | acab.naiveha.subrosa |
| Author: | naive-HA |
| License: | Apache-2.0 |
| Donation: | Bitcoin |
| InRepoSince: | 2026-03-11 |
| LastRepoUpdate: | 2026-11-17 |
| LastAppUpdate: | 2026-11-17 |
| LastVersion: | 3.0.0 |
| Categories: | Security |
| APK source: | Github |
| Google Play: | Check if it's there |

Turn your Android phone into an on-the-go security command center for your hardware keys. Type ultra-secure passwords on any computer without touching the keyboard. Program OpenPGP identities on the fly. Wipe secrets instantly.
Picture this: you are sitting at a bustling coffee shop, library, or airport gate with surveillance cameras overhead and people nearby. You need to log into a 32-character master password, your BitLocker/LUKS encrypted drive, a work laptop, or a remote server. Typing it out invites shoulder surfers, camera recording, and hardware keyloggers. Leaving that password permanently stored on your physical security key means losing your keychain compromises your account.
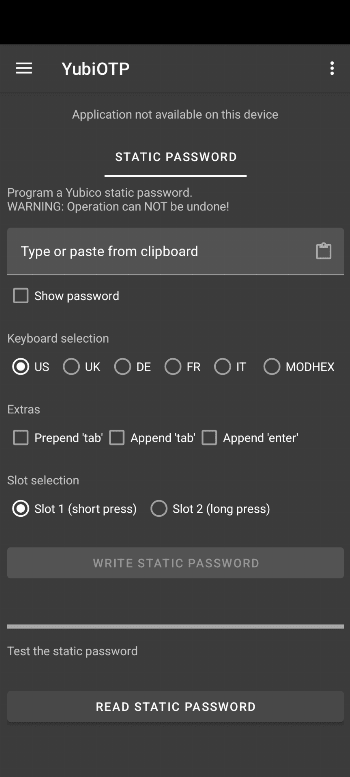
With sub rosa, you get the best of both worlds: tap your NFC security key (or plug via USB) to your Android phone to load the password or OpenPGP key you need right now. Plug the key into any PC, Mac, server, or kiosk. Touch the gold contact. The hardware key acts as a standard USB keyboard (HID) and types your long, complex password in milliseconds. Done with your session? Tap the key to your phone again to erase it. If you lose your physical key on the train, it holds zero data.
International Keyboard Layouts Supported
* US: space, \n, \t and abcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ0123456789!"#$%&'()+-=,./:;<>?@\][^_{}|~* **UK**: space,\n,\tandabcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ0123456789!@£$%&'()*+-=,./:;<>?"#][^_{}~¬
* DE: space, \n, \t and abcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ0123456789!"#$%&'()*+-=,./:;<>?^_§´ÄÖÜßäöü* **FR**: space,\n,\tandabcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ0123456789!"$%&'()+-=,./:;<_£§°²µàçèéù* **IT**: space,\n,\tandabcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ0123456789!"#$%&'()*+,-./:;<=>?@\^_|£§°çèéàìòù
* MODHEX: bcdefghijklnrtuvBCDEFGHIJKLNRTUV
Picture this: you need to handle high-stakes digital tasks on the move. In the morning, you must sign a legally binding contract or authenticate an emergency SSH session into a remote production server. In the afternoon, you need to decrypt a confidential, business-critical document received from a business partner. Later, as an investigative journalist, activist, or privacy advocate, you need to encrypt a sensitive whistleblower document before transmitting it to a news organization.
Keeping these distinct digital identities and private keys permanently stored on a single physical key on your keychain is a disaster waiting to happen. If you lose that key on a train or it gets searched at a border crossing, all your compartmentalized personas are exposed. Carrying half a dozen separate, expensive hardware tokens everywhere is clunky and impractical.
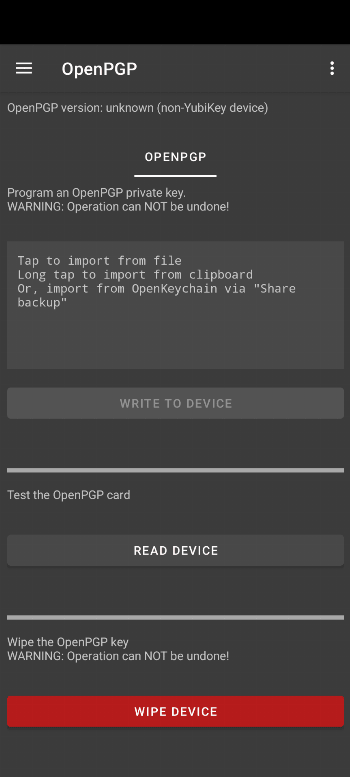
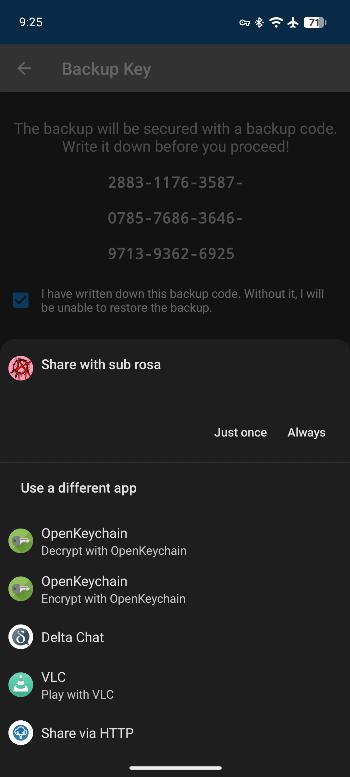
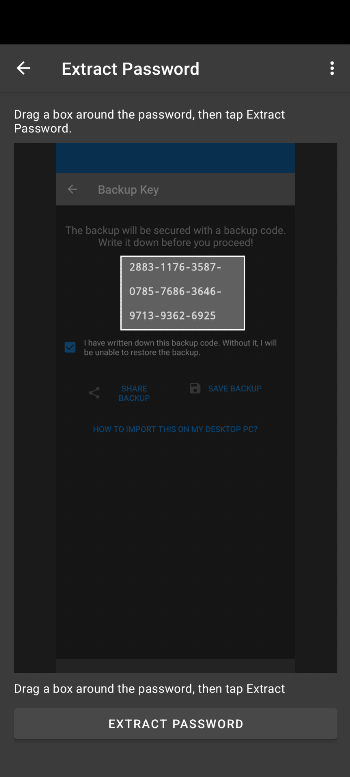
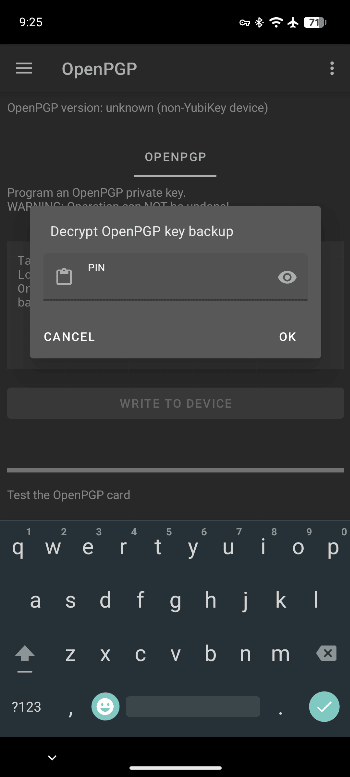
With sub rosa, your hardware key becomes a disposable, on-demand cryptographic badge: manage your OpenPGP identities safely in apps like OpenKeychain or PGPony on your phone. When a specific task arises, tap your YubiKey, Nitrokey, or Librem Key via NFC or USB to flash the exact Signing, Decryption, or Authentication subkeys (RSA, Ed25519, X25519) you need for that single moment. Sign the document, decrypt the partner’s message, or encrypt the whistleblower report. Once you're done, wipe the hardware key clean with another tap. If anyone picks up your security key later, it holds zero data. One physical key, infinite ephemeral identities.
On-the-Go OpenPGP Management Program OpenPGP keys (RSA, NIST P-curves, Brainpool, Ed25519, X25519) onto